ISO standards for AI: what to use and how to comply (2026 update)
In this article
This article was originally published 08-11-2024, last updated on 22-10-2026.
Summary
ISO and IEC publish a portfolio of globally recognized standards, this article highlights the relevant standards for artificial intelligence (AI).
This article explains what each standard does, how they fit together, and how to start adopting them.
ISO standards for AI overview
| 🔗 ISO standard | Description | Price |
|---|---|---|
|
ISO 27090 provides guidance on understanding, detecting and mitigating security threats specific to artificial intelligence (AI) systems throughout their life cycle. It explains how vulnerabilities can be exploited, what the consequences can be and which measures can help address them. |
CHF 204
~€220/$246 |
|
|
ISO 42001 is an international standard that specifies requirements for establishing, implementing, maintaining, and continually improving an Artificial Intelligence Management System (AIMS) within organizations. It is designed for entities providing or utilizing AI-based products or services, ensuring responsible development and use of AI systems. |
CHF 155
~€242/$272 |
|
|
This document provides guidance on how organizations that develop, produce, deploy or use products, systems and services that utilize artificial intelligence (AI) can manage risk specifically related to AI. The guidance also aims to assist organizations to integrate risk management into their AI-related activities and functions. It moreover describes processes for the effective implementation and integration of AI risk management. |
CHF 155
~€167/$187 |
|
|
ISO 22989 establishes terminology for AI and describes concepts in the field of AI.
This document can be used in the development of other standards and in support of communications among diverse, interested parties or stakeholders. |
CHF 0
~€0/$0 |
|
|
ISO 5338 defines a set of processes and associated concepts for describing the life cycle of AI systems based on machine learning and heuristic systems.
|
CHF 181
~€195/$218 |
|
|
ISO 23053 defines a set of processes and associated concepts for describing the life cycle of AI systems based on machine learning and heuristic systems.
|
CHF 196
~€211/$236 |
|
|
ISO 24028 provides an overview of trustworthiness characteristics such as reliability, safety, security, privacy, and resilience.
|
CHF 196
~€211/$236 |
|
|
ISO 25059 outlines a quality model for AI systems and is an application-specific extension to the standards on SQuaRE. The characteristics and sub-characteristics detailed in the model provide consistent terminology for specifying, measuring and evaluating AI system quality.
|
CHF 100
~€107/$120 |
Disclaimer: Prices in this article come from the ISO Store, which lists them in Swiss francs (CHF). We converted them to euros and US dollars at the exchange rate on October 22, 2026, the date we last updated this article. Prices can change, so check the ISO Store for the current price.
What is ISO/IEC?
ISO/IEC stands for the joint partnership between the International Organization for Standardization (ISO) and the International Electrotechnical Commission (IEC).
Together, these two independent bodies create and publish globally recognized international standards for information technology, electronics, and business processes.
What is ISO?
ISO, the International Organization for Standardization, brings together global experts to agree on the best way of doing things, from making a product to managing a process. It is one of the oldest non-governmental international organizations. ISO was formally established in 1947, and it has supported trade and cooperation between people and companies worldwide ever since. Its standards exist to make lives easier, safer, and better.
What is IEC?
The International Electrotechnical Commission (IEC) prepares and publishes international standards for all electrical, electronic, and related technologies. When you see “ISO/IEC” in a standard’s name, the two bodies developed it jointly. AI standards carry this label because they come out of ISO/IEC JTC 1, the joint technical committee for information technology
Is ISO compliance a legal requirement?
No. ISO standards are voluntary. That said, they align naturally with regulations across industries, so working toward them often makes legal obligations easier to meet.
ISO compliance is highly regarded in the global business community because it shows an organization’s commitment to quality and industry practice.
For AI compliance, these standards give teams, suppliers, and auditors a common baseline.
That said, if you’re looking for a regulatory overview, please see:
Key ISO standards for AI you should know
Securing AI systems: ISO/IEC 27090
ISO 27090 is the newest edition and was published in October 2026.
It provides guidance on understanding, detecting and mitigating security threats specific to artificial intelligence (AI) systems throughout their life cycle.
It explains how vulnerabilities can be exploited, what the consequences can be and which measures can help address them.
This ISO standard is special to us, as Software Improvement Group has contributed to its creation.
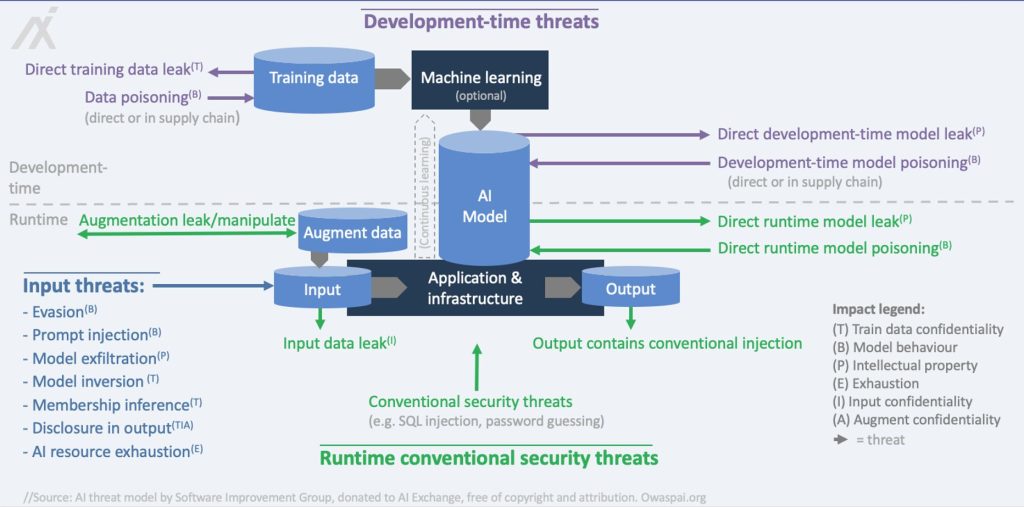
The diagram we added below shows the threat map we originally donated to the OWASP AI Exchange and was accepted into ISO/IEC 27090.
It addresses security threats and compromises to AI systems across the full lifecycle, from training data to the model itself. For each threat, it describes how attackers exploit the weakness, what damage results, and which countermeasures reduce the risk.
For organizations developing or using AI, the standard helps identify what needs protecting, from training data to AI models.
It addresses threats such as data poisoning and model theft, while recognizing that established cybersecurity practices remain essential.
Or as our CAIO and co-founder of the OWASP AI Exchange, Rob van der Veer, said:
“I’d like to call on everybody building or deploying AI systems, please:
threat model your AI systems, analyse your risks, and choose and implement countermeasures wisely. It may feel slower, but you’ll reach your destination faster by avoiding trouble along the way.”
It complements ISO/IEC 27001, the information security management system standard, and ISO/IEC 27002, because established security practices still matter. It shows where AI needs more. Our AI Maturity Guide gives security teams the same advice: extend your existing security management system with AI-specific assets, threats, and controls instead of securing AI separately.
But the ISO/IEC 27090 isn’t the only AI-specific standard. let’s take a look at the other examples.
AI Governance: ISO/IEC 42001 and ISO/IEC 23894
You could say, these are foundational standards when it comes to AI.
ISO/IEC 42001: The AI management system
ISO/IEC 42001, often called ISO 42001, is the certifiable management system standard for AI. The ISO 42001 requirements ask you to set the scope and policy for AI use and to assign roles and accountability. You run risk and impact assessments, manage the data and model lifecycle, and govern third parties. You also monitor systems in production and keep improving.
If you already run ISO/IEC 27001, you will recognize the Plan-Do-Check-Act cycle and many of the integration points. The comparison later in this section shows how the two fit together
Certification with ISO 42001 shows that responsible AI practices apply across the organization.
This is also something we mention in our AI Maturity Guide 2026; the board sets up the foundations for the AI management system, and governance, risk, and compliance (GRC) leaders run it. The guide’s advice is to extend existing governance and roles instead of building a separate AI organization.
ISO/IEC 23894: AI risk management
ISO 23894 provides a risk process tailored to AI. It guides you to map the system context and its stakeholders and to identify harms such as bias, security, privacy, and safety issues. You then evaluate likelihood and impact, choose controls, and monitor the residual risk. Use this standard to support ISO 42001, to inform go-live decisions, and to stay consistent with external frameworks like NIST AI RMF.
ISO/IEC 42001 vs ISO/IEC 27001: How they differ and fit together
ISO/IEC 27001 is an information security management system (ISMS) for the entire organization. ISO/IEC 42001 is an an AI management system (AIMS) for AI systems and their lifecycle risks.
Both follow Plan-Do-Check-Act and both can be audited, here’s how they differ:
- Scope: 27001 protects information assets across the business. 42001 governs AI use cases, data, models, and operations.
- Controls: 27001 Annex A targets security controls. 42001 requires AI-specific controls such as data governance for training, model risk assessment, validation, human oversight, and drift monitoring.
- Risk: 27001 prioritizes confidentiality, integrity, and availability. 42001 extends risk to bias, explainability, safety, compliance and societal impact, supported by ISO/IEC 23894.
In practice, you align them. Bring AI assets into the ISMS, apply AI-specific governance through the AIMS, and reuse shared processes such as incident management and supplier oversight. ISO/IEC 27090, covered above, adds guidance on AI-specific security threats.
Building AI: terminology, lifecycle, architecture, and quality
ISO/IEC 22989: AI concepts and terminology
ISO/IEC 22989 defines the vocabulary of AI, including training data, model, inference, explainability, and human-in-the-loop. Using it keeps policies, control descriptions, and supplier contracts unambiguous, which matters when you audit or certify against 42001.
ISO/IEC 5338 – AI system lifecycle processes
ISO/IEC 5338 standardizes lifecycle processes for AI systems, from requirements and data readiness to verification, validation, deployment, monitoring, and retirement. It complements regular software engineering practice and sets checkpoints for data provenance, model testing, drift monitoring, and human oversight.
Just like the new ISO/IEC 27090, this one is also special to us, as we contributed to the development of the ISO/IEC 5338, and Rob van der Veer, led its writing group. SIG applies the standard in assessments and coaching.
For a deeper dive, see ISO 5338: the global standard on AI systems. To understand our contributions, read Our role in ISO/CEN/NEN AI standardization.
ISO/IEC 23053 – Framework for AI systems using machine learning
ISO/IEC 23053 describes the components of a machine learning based AI system and the function each one performs. It shows how datasets, training pipelines, models, serving layers, and feedback loops fit together.
Use it to structure documentation and to align engineering with the governance expectations in 42001 and 23894.
ISO/IEC 25059 and ISO/IEC TR 24028: quality and trust
ISO/IEC 25059 extends the quality model for software to AI systems. It gives you attributes and measures for requirements and acceptance. ISO/IEC TR 24028 is a technical report that surveys trustworthiness characteristics such as reliability, safety, security, privacy, and resilience, along with methods to assess them. Use 25059 to set quality targets and 24028 to set trust goals.
A practical framework for adopting ISO standards for AI
The steps below give you a starting point. Most organizations work on several in parallel, depending on their starting point and existing governance.
Our AI Maturity Guide gives board members, CTOs, CISOs, and GRC leaders 20 practical steps on AI governance, risk, development, and security.
- Map AI use cases and risks Build an inventory of current, planned, and informal AI use, including AI-assisted development tools, and classify impact using ISO/IEC 23894. Extend the inventories you already have instead of starting from zero.
- Establish governance
Define your AIMS scope, roles, and policies under ISO/IEC 42001, with human oversight and accountability built in. Assign AI work to existing roles where you can. - Engineer the lifecycle
Use ISO/IEC 5338 to extend your existing software lifecycle for AI. Use ISO/IEC 23053 to describe the system’s components, ISO/IEC 25059 for quality targets, and ISO/IEC TR 24028 for trust goals. - Secure the system
Add AI assets, threats, and controls to your existing ISO/IEC 27001 security management system. Run AI threat modeling for each system and select countermeasures using ISO/IEC 27090. - Apply and measure
Put data governance, model validation, drift and bias monitoring, and change management into daily practice. Treat AI maturity as a program with a roadmap, and report progress with a few clear metrics, such as the percentage of practices assigned and active. Check audit readiness and track corrective actions.
FAQs
Is there an ISO standard for artificial intelligence?
Yes, there is a portfolio. ISO/IEC 42001 is a certifiable management system for AI, ISO/IEC 23894 covers risk management, and ISO/IEC 22989 defines terminology. ISO/IEC 5338, 23053, 25059, and 27090 cover lifecycle, architecture, quality, and security. Use 42001 to govern and audit your AI program, and the others to shape lifecycle, risk, quality, and security.
Which ISO covers AI?
ISO/IEC JTC 1/SC 42 develops most AI standards. AI security guidance comes from ISO/IEC JTC 1/SC 27, which covers information security and cybersecurity. A good starting set for most organizations is ISO/IEC 42001, 23894, 22989, 5338, 25059, and 27090.
What is ISO 42001, the international standard for AI management systems?
ISO/IEC 42001 sets certifiable requirements for an AI management system, including policies, roles, risk management, human oversight, and continual improvement.
Can you get ISO 42001 certified?
Yes. ISO/IEC 42001 is a certifiable management system standard. ISO/IEC 27090 is a guidance standard, so you cannot certify against it.
Is there an ISO standard for AI security?
Yes. ISO/IEC 27090, published in October 2026, gives guidance on the security threats that target AI systems and the countermeasures that reduce the risk. It is a guidance standard, so you cannot certify against it.
Can you get certified for the ISO AI security standard?
No. ISO/IEC 27090 is a guidance standard, so you cannot certify against it. Individuals can get certified in AI security, though. The EXIN AI Security Professional (AISP) certification is for individual professionals.
Rob van der Veer, SIG’s Chief AI Officer and founder of the OWASP AI Exchange, wrote the courseware, drawing on years spent teaching this material to security teams worldwide.
It covers organizing AI security in the enterprise, implementing controls, and testing AI systems for security. It is built on the OWASP AI Exchange and co-developed by Software Improvement Group.
Did Software Improvement Group write any of the ISO standards for AI?
SIG contributed to two of them. ISO standards are developed by international groups of experts, so no single company writes one. For ISO/IEC 5338, SIG contributed to its development, and Rob van der Veer, SIG’s Chief AI Officer, led its writing group. For ISO/IEC 27090, Rob contributed as an expert member and author, and the AI threat model SIG originally donated to the OWASP AI Exchange was accepted into the standard. Contributions from the AI Exchange helped speed up its completion.
Is ISO compliance a legal requirement?
No. ISO standards are voluntary, but they align with many regulations and can make legal obligations easier to meet.